At AMLYZE, our commitment to security has never been an afterthought – it has been our foundation from day one.
Our engineering and product teams come from backgrounds in core banking, infrastructure, and enterprise-grade systems, where stability, controlled processes, and robust security are mandatory. These principles guide every architectural decision we make.
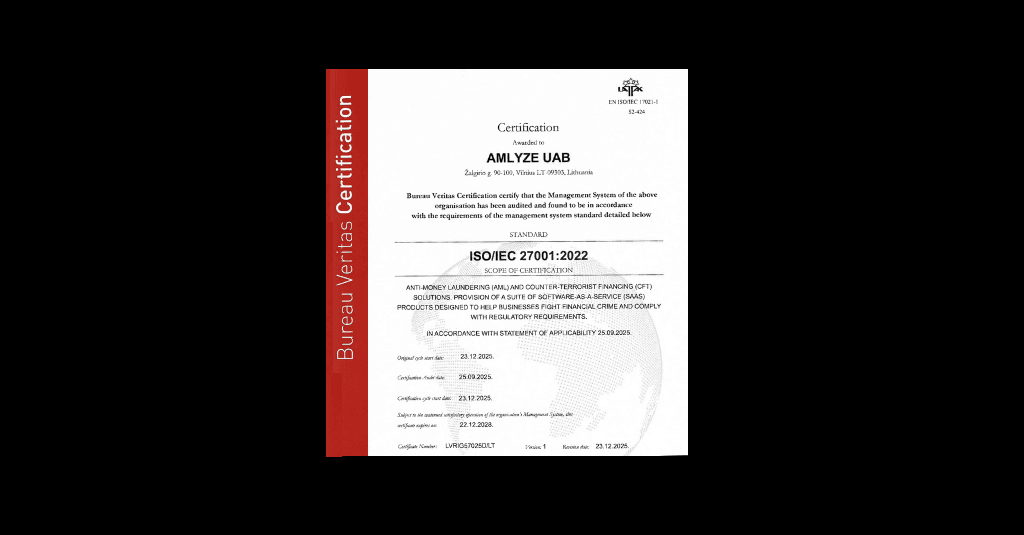
Today, we are proud to announce that this approach has once again been validated: AMLYZE is now officially ISO 27001 certified by Bureau Veritas Group.
This certification confirms that AMLYZE adheres to globally recognized standards for information security management systems (ISMS) – a requirement increasingly expected by banks, fintechs, EMIs, crypto institutions, and other regulated entities.
And it fits within a broader security and compliance framework.
In addition to ISO 27001:
-
AMLYZE is fully GDPR compliant, ensuring personal data is processed securely, lawfully, and transparently.
-
AMLYZE aligns with DORA (Digital Operational Resilience Act) requirements, demonstrating operational resilience, business continuity preparedness, and robust ICT risk management – especially critical for EU-regulated financial institutions.
Together, these frameworks reinforce our commitment to offering solutions that are not only powerful but safe, resilient, and trustworthy.
A message from our CEO and Co-Founder, Gabrielius Erikas Bilkštys:
Security isn’t a milestone – it’s a discipline. ISO 27001 is not just a certificate on a wall for us. It’s a formal validation of the standards we’ve upheld since the very beginning. With GDPR and DORA compliance also embedded into our processes, our customers can trust that AMLYZE is built on solid, resilient, and transparent foundations.”
– Gabrielius Erikas Bilkštys, CEO & Co-Founder, AMLYZE